
We secure your digital world.
Every organization has weaknesses. The only question is who finds them first.

Experienced. Dedicated. Certified.
To stay ahead in a field that changes weekly, every certified member of our staff completes a minimum of fifty hours of continuing education each year. Offensive security is not a credential you earn once. It is a practice you keep current or lose.
Accredited and affiliated


- OSCP
- OSCE
- GPEN
- GWAPT
- CISSP
- CISA
- CEH
- CRTO
- AWS Security
- Azure Security

Cyber threats know no borders. Neither do we.
We protect businesses, organizations, and critical infrastructure worldwide, delivering penetration testing tailored to each region's regulatory and threat landscape. We have worked with enterprises, startups, and government agencies across multiple continents.
Sectors we serve
- Healthcare
- Manufacturing
- Finance
- Technology
- Artificial Intelligence
- Education
- Government
You are hiring practitioners, not a logo.
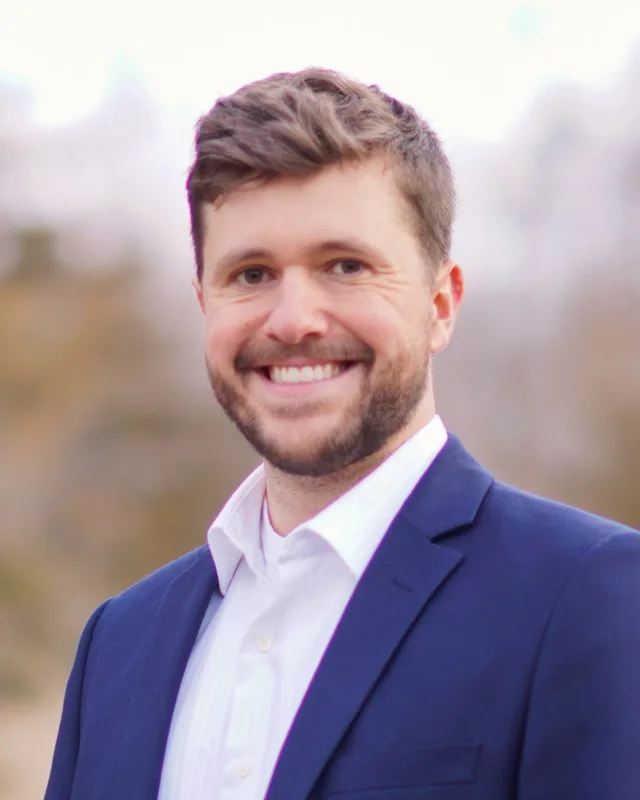
Before founding Vigilant, Nathan led the offensive security team at one of the top consulting firms in the United States, running internal and external network testing, web and API assessments, social engineering, and wireless work for clients across healthcare, finance, manufacturing, and government.
He built Vigilant to do the work the way he believes it should be done: a small number of engagements at a time, senior people on every one, and enough hours in each to chase a finding to its conclusion rather than close the ticket and move on. The interesting problems are never the ones a scanner hands you, and they are never found in a hurry.
Nathan has consulted for more than 450 companies. He holds a master's in Cyber Defense and a bachelor's in Cyber Operations from Dakota State University, held the top 1% on Hack The Box, contributes to their content library, and mentors through EC-Council. He is a member of InfraGard and the Cybersecurity Council of South Dakota.
- CISSP
- CEH
- CCSK
- CC
- M.S. Cyber DefenseDakota State University
- B.S. Cyber OperationsDakota State University
What our clients say.
Client names are withheld by agreement. Security vendors should not publish their customers' attack surface.
We partnered with Vigilant Cybersecurity to enhance our cybersecurity measures, and the results have been outstanding. Their elite team provided top-notch network penetration testing, significantly fortifying our business against potential threats. We highly recommend their services to organizations looking to strengthen their cybersecurity defenses.
Average client rating across engagements. Every assessment ends with a retest and an attestation letter.
- Retest
- Included
- Attestation
- Issued
Four principles we don't negotiate.
Offensive security is a trust business. These are the commitments that earn it, and the reason clients come back rather than re-bid every year.
We test by hand
Automation has a place. It is the first hour of the engagement, not the deliverable. Everything we report has been validated by a person who confirmed it is genuinely exploitable in your environment.
We report impact, not inventory
A list of CVEs is not a security assessment. We tell you what an attacker could actually do, which assets they would reach, and which three fixes eliminate the most risk for the least effort.
We stay until it's fixed
Retesting is included, not upsold. An engagement is not finished when the report is delivered. It is finished when the findings are closed and verified closed.
We tell you when you don't need us
If a scoping call reveals that what you actually need is a vulnerability management process rather than a pentest, we will say so. It costs us a sale and earns the next three.
Don't wait for a breach.
Find out what an attacker could reach before one tries. Scoping calls are free, take about thirty minutes, and end with fixed pricing.